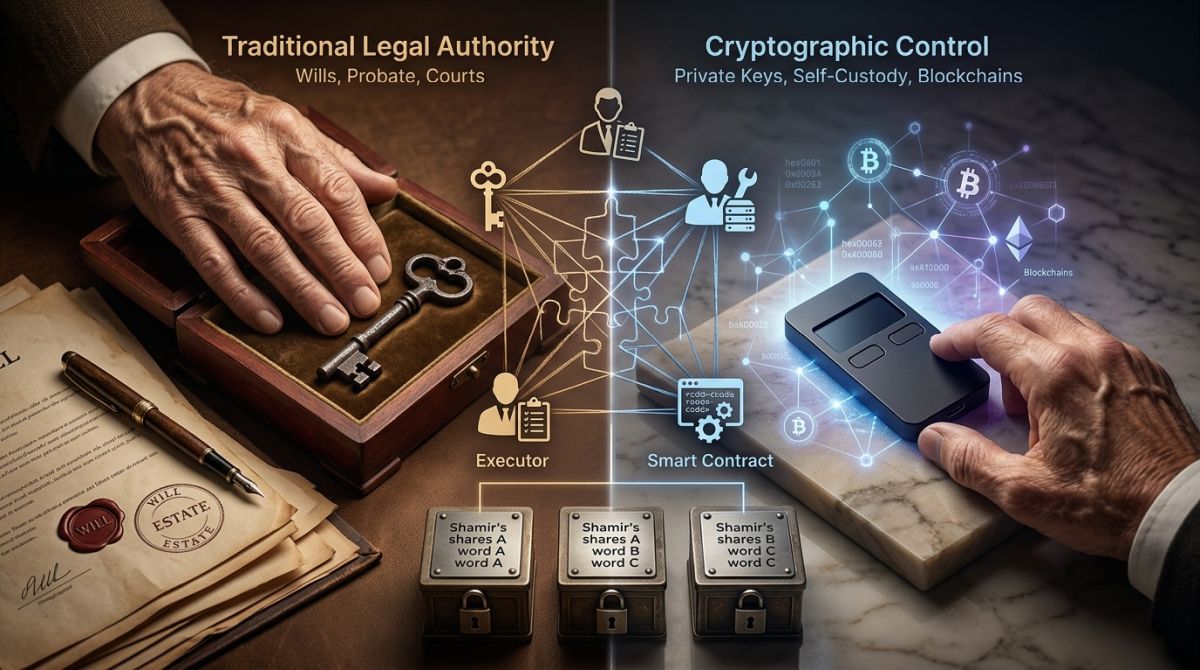
Crypto inheritance plans fail when legal ownership and cryptographic control are treated as the same thing.
As an economist and former banker with 25 years in traditional finance, I’m used to a system where legal documents give a financial institution a process to follow. An executor presents the required paperwork, the institution reviews the claim, and assets can eventually be transferred.
Self-custody changes that relationship.
Inheritance and probate law determine who is entitled to a deceased person’s property. A blockchain checks whether a transaction satisfies its required signatures and other spending conditions. It does not read wills, recognize death certificates, follow probate court orders, or automatically transfer a wallet to a named beneficiary.
That means an executor can have legal authority over cryptocurrency without being able to move it. Conversely, someone who obtains the necessary signing keys may be able to transfer assets without having any legal right to them.
A noncustodial wallet, also called a self-custody wallet, is not an account that a company can simply unlock. The assets are recorded on the blockchain. The wallet manages the keys used to authorize transactions. If those keys and every valid recovery path are lost, there may be no password reset, customer support department, or court order capable of reconstructing them.
The practical solution is not to put a seed phrase in a will or arrange for a cloud service to email it after a few months of inactivity. A reliable crypto inheritance plan separates four things:
- Legal authority.
- Asset discovery and identification.
- Cryptographic recovery.
- Controlled transfer or liquidation.
In this guide, I’ll explain how to build that system without expecting your heirs to become cybersecurity specialists.
This is operational guidance, not individualized legal or tax advice. Probate, trust, property, and fiduciary laws vary by jurisdiction. An attorney should adapt the legal structure to the laws affecting the owner, estate, trust, executor, and beneficiaries.
What Happens to a Self-Custody Crypto Wallet When You Die?
A person’s death does not, by itself, trigger a transfer on the blockchain.
Your existing addresses and their spending conditions do not expire because you have died. Assets remain recorded on-chain. Smart contracts continue operating according to their code when transactions or other supported execution mechanisms interact with them.
Staking positions, collateralized loans, liquidity positions, and time-locked assets can remain active. Some positions may continue earning rewards, accruing debt, or facing liquidation while the family is still trying to understand what exists.
The blockchain has no built-in way to know that the person controlling the keys has died.
What happens next depends on the custody model.
| Question | Custodial exchange or provider-managed wallet | Self-custody wallet |
|---|---|---|
| Who controls the keys? | The provider or its custody arrangement | The wallet owner and any designated signers |
| Can a company restore access? | Potentially, subject to its procedures and applicable law | Usually not; recovery must follow the wallet’s existing design |
| Can an executor submit legal documents? | Usually, although requirements vary | There may be no provider to contact |
| What ultimately authorizes a transfer? | The provider’s internal systems and approval process | The required cryptographic signatures and other spending conditions |
| Main inheritance risk | Finding the account, completing the legal process, and navigating provider restrictions | Permanent loss of keys or unauthorized use of them |
With a custodial account, an executor may be able to provide a death certificate, court-issued appointment documents, trust records, and other evidence to the provider. The provider may arrange an authorized transfer or liquidation rather than give the executor the deceased person’s login credentials.
With a self-custody wallet, those documents establish authority, but they do not produce a valid blockchain signature. Someone still needs the appropriate private keys, recovery materials, signing devices, and wallet configuration.
That creates two distinct forms of control:
- Legal control: The right to administer or inherit the assets.
- Technical control: The ability to create a valid transaction.
When I evaluate a crypto inheritance plan, I look for both. One without the other is an incomplete plan.
Why a Traditional Will Is Not Enough for Crypto Inheritance
A will is a legal instruction, not a key-recovery mechanism.
In a typical probate proceeding, the original will is filed with the court. The court determines whether the document is valid and appoints an executor or personal representative. That person identifies estate assets, addresses debts and tax obligations, and distributes the remaining property.
For example, New York’s probate process for an estate with a will involves submitting the original will, a death certificate, a probate petition, and supporting documents to Surrogate’s Court.
Under Massachusetts rules for access to probate court records, estate-related proceedings are generally public unless a case, document, or particular information is restricted or impounded.
California’s guidance on requesting public court records similarly explains that case records are maintained by the court where the case was filed. Public access does not necessarily mean that every document is freely searchable online, but it does mean you should not assume a court filing is confidential.
Other jurisdictions have their own filing and access rules. The broader point remains: wills and probate records often become available for inspection or copying.
That makes a standard will one of the worst places to disclose:
- A private key.
- A seed phrase or recovery phrase.
- A hardware wallet PIN.
- A BIP39 passphrase.
- Enough secret shares to satisfy a recovery threshold.
- An encrypted seed phrase together with the instructions needed to decrypt it.
A recovery phrase is not just another password. It can serve as the root credential for an entire family of accounts and addresses. If no additional factor is required, anyone who obtains it may gain control of the associated assets.
Publishing that phrase in a probate record is closer to publishing a signed blank check than publishing an account number.
Even when a probate file cannot be searched online, it may still be accessible at the courthouse or copied by authorized participants. Every person and system that handles the document becomes part of your security perimeter.
Public Wallet Addresses Are Not Private Keys, but They Are Still Sensitive
A public wallet address generally cannot be used on its own to spend assets. On transparent blockchains, however, it can reveal balances, transaction history, transaction counterparties or connections, token holdings, protocol positions, and future transfers involving that address.
Putting a high-value address in a will can turn a probate file into a list of potential targets.
Criminals may use that information to identify beneficiaries, monitor estate activity, impersonate wallet support staff, or send phishing messages just as the inheritance process begins.
I treat public addresses as sensitive inventory information. They are not signing secrets, but that does not make them harmless to publish.
What a Will or Trust Should Include
Estate documents should establish authority and express the owner’s intentions without exposing the keys.
Depending on local law and the owner’s circumstances, an attorney may need to address a fiduciary’s authority to:
- Access and secure digital devices.
- Manage digital assets and virtual currencies.
- Access custodial accounts and associated records.
- Hire qualified legal, tax, security, or blockchain specialists.
- Pay network, custody, storage, and transaction fees.
- Transfer assets in kind.
- Liquidate assets when appropriate.
- Manage staking, lending, collateral, governance rights, and protocol positions.
- Obtain tax and transaction records.
- Establish temporary custody on behalf of the estate or trust.
- Distribute assets to beneficiaries.
- Act during the owner’s incapacity as well as after death, through the appropriate legal instruments.
That last point requires careful drafting. A will does not authorize someone to act during your lifetime. Incapacity planning may require a trust, durable power of attorney, or other jurisdiction-specific arrangement. An agent’s authority under a power of attorney generally ends at death, when the appropriate estate or trust authority takes over.
The documents can acknowledge a separate digital-asset inventory or inheritance memorandum. They should not contain the recovery secrets themselves.
The legal effect of a separate memorandum varies. It may be an administrative guide rather than a binding document that determines who receives property. An estate-planning attorney should decide how it is referenced, stored, authenticated, updated, and delivered.
Digital-Asset Laws Cannot Recreate Private Keys
The Revised Uniform Fiduciary Access to Digital Assets Act, commonly called RUFADAA, provides a model state-law framework for fiduciary access to digital assets, including virtual currencies and online accounts.
It also addresses when service providers may disclose digital assets or electronic communications. State enactments, user directions, consent requirements, service terms, and other applicable laws can affect what a fiduciary actually receives.
That framework can help when a company controls the relevant account or information.
It does not solve the cryptographic problem of self-custody.
With a noncustodial wallet, there may be no provider capable of disclosing or resetting anything useful. The law can identify the person authorized to act. The blockchain still requires the appropriate signatures.
A properly established and funded trust may improve continuity and reduce probate exposure for assets held by the trust. It does not eliminate the need for a tested recovery process.
A successor trustee without the keys has the same technical problem as an executor without the keys.
The Security Problem Behind Crypto Inheritance
A crypto inheritance plan must protect against theft during your lifetime and permanent loss after your death.
Those are not the same problem, and solving one carelessly can make the other worse.
A workable plan must account for:
- Theft while the owner is alive.
- Permanent loss after death.
- Premature access by beneficiaries or insiders.
- Destruction of the only physical backup.
- Loss of a passphrase or wallet configuration.
- Confusion about networks, accounts, or derivation paths.
- Hardware failure or software obsolescence.
- Executor mistakes.
- Phishing attacks during bereavement.
- Legal disputes among beneficiaries.
- Incomplete tax and transaction records.
- Excessive complexity that makes the plan impossible to execute.
These risks pull in different directions.
Giving one person the complete recovery phrase today makes inheritance easier, but weakens lifetime security. Preventing everyone from accessing the key until death requires some person, institution, or system to determine when access should be released.
Requiring every share makes collusion harder, but losing one share can destroy the recovery path. Requiring too few shares makes recovery more convenient, but also makes coordinated misuse easier.
Without a trusted third party or additional technical assumptions, no mechanism can simultaneously guarantee all three of the following:
- Nobody except the owner can access the assets before the owner dies.
- Beneficiaries can access the assets immediately after death.
- No person or institution is trusted to establish that the death occurred.
A realistic plan accepts that trade-off. It combines legal authority, threshold access where appropriate, independent storage locations, and human verification.
I would rather see a family understand those compromises than rely on a product marketed as completely automatic or completely trustless.
Why Dead Man’s Switches Can Fail in Crypto Inheritance
Inactivity is not proof of death, which makes an automated dead man’s switch a risky way to release wallet keys.
A typical dead man’s switch works like this:
- The owner stores a secret or configures an automated transaction.
- The owner must periodically check in to confirm continued activity.
- If the check-in does not happen, the system releases information or allows assets to move.
The idea is appealing because it replaces probate delays with automation. The difficulty is deciding what a missed check-in actually means.
False Triggers
A living owner may miss a check-in because of:
- Hospitalization.
- Extended travel.
- Detention or incarceration.
- Loss of a phone or security key.
- Email filtering.
- Account suspension.
- Forgotten calendar reminders.
- Cognitive decline.
- A changed phone number.
- Authentication failure.
- A natural disaster or communications outage.
If the system releases a private key, an incorrect trigger can expose the entire wallet. A grace period can reduce that risk, but it cannot turn inactivity into reliable evidence of death.
Failure to Trigger After Death
The opposite can happen, too. A system may fail to activate after the owner dies because:
- A device remains logged in and continues synchronizing.
- An email client keeps checking messages.
- An automated process registers account activity.
- A family member uses the owner’s computer.
- The service mistakes background activity for human activity.
- An attacker compromises the account and deliberately keeps it active.
Google explains that its Inactive Account Manager uses several account-activity signals, including recent sign-ins, activity recorded in My Activity, Gmail use, and Android check-ins.
Depending on the service and device behavior, background activity can complicate the interpretation of whether an account is genuinely inactive.
That makes an inactivity service useful for notifications and selected data sharing. It does not make it a dependable way to establish that someone has died.
Dependence on a Cloud Provider
A cloud-based switch depends on much more than the owner’s original instructions. It may require that:
- The provider continues offering the feature.
- The account remains open.
- Account-recovery addresses remain valid.
- The recipient keeps the same phone number.
- The provider correctly authenticates the recipient.
- Stored file formats remain readable.
- Data is not deleted under inactivity policies.
- Service terms and legal requirements remain compatible with the plan.
Those can be acceptable dependencies for reminders or document delivery. They are dangerous dependencies for the only copy of a seed phrase.
Smart-Contract Risks
A smart contract can enforce a timer, a guardian approval process, or recovery rules.
Systems built around account abstraction and smart-contract wallets can support flexible security policies, multiple guardians, and programmable access. Those features may be useful for inheritance when they are deliberately implemented, professionally reviewed, and maintained.
They still do not independently know that a person has died.
They know only that:
- A timer expired.
- A particular key did not check in.
- The required number of guardians approved a request.
- An oracle supplied a particular assertion.
- A predefined transaction condition was satisfied.
A timer reaching its deadline may simply make an action executable. A transaction, relayer, or other execution mechanism may still be needed to carry it out.
A contract can also contain a vulnerability, depend on an upgrade key, relayer, or oracle, or behave unexpectedly when interacting with another contract.
As the guidance on smart-contract security explains, contracts can control substantial value while exposing users to access-control, logic, oracle, and integration failures. Fixing deployed code can be difficult or impossible, depending on the design.
Programmable recovery can be valuable. It is not the same as removing trust, operational risk, or maintenance.
A New Opening for Phishing
Periodic check-ins create a recurring, predictable security ritual. Attackers can imitate:
- “Confirm you are still alive” messages.
- Wallet-verification notices.
- Guardian approval requests.
- Cloud-service login pages.
- Hardware wallet update requests.
- Smart-contract recovery transactions.
Someone expecting an inheritance-related message on a particular schedule may be more likely to trust a convincing fake.
The practical guidance on wallet security and scam prevention reinforces a rule I would put in every family’s instructions: legitimate support does not need your recovery phrase or private keys to help you.
The Right Role for Automation
Automation can help with:
- Reminding the owner to review the plan.
- Notifying an attorney or family member after extended inactivity.
- Delivering an instruction packet that contains no secrets.
- Identifying the executor and attorney.
- Starting a human verification process.
- Confirming that an asset inventory exists.
It should not automatically publish a complete seed phrase, private key, or enough shares to satisfy the recovery threshold.
My rule is straightforward:
Use automation to start the inheritance process, not to complete the cryptographic handover.
A Practical Four-Step Crypto Inheritance Protocol
The most dependable crypto inheritance plan is a tested process that separates authority, information, recovery, and transfer.
No inheritance system is literally foolproof. The closest practical alternative is a fault-tolerant plan with no secrets in public records, no single physical point of failure, and no step that forces a grieving beneficiary to improvise.
The following four-step protocol is designed for people who are not developers. It can be adapted to a modest hardware wallet or a substantial portfolio.
The right implementation depends on the assets, networks, family, legal structure, and custody risks involved.
Step 1: Establish Legal Authority and Build a Nonsecret Asset Map
Start by documenting who can act, what exists, and where the recovery components are held, without placing spending secrets in the same document.
First, separate the roles of the people involved.
A plan may include:
- Owner: The person who currently controls the assets.
- Fiduciary: The executor, personal representative, or successor trustee with legal authority.
- Technical operator: A trusted person or professional who understands wallet recovery.
- Recovery-share holders: People or institutions holding individual recovery shares.
- Beneficiaries: The people legally entitled to receive the assets.
- Attorney and tax professional: Advisers responsible for the legal and tax issues.
For a high-value portfolio, one person should not automatically fill every role.
A beneficiary may not be the best executor. An executor may not know how to operate a hardware wallet. A technical operator should not be allowed to work alone with enough recovery material to control the assets.
In traditional finance, we call this separation of duties. I see no reason to abandon that discipline simply because the assets are on a blockchain.
Create Three Separate Information Layers
Layer 1: Estate documents
These establish who has authority and who receives the property. They contain no private keys, seed phrases, PINs, passphrases, or secret shares.
Layer 2: Restricted asset and recovery map
This tells the authorized fiduciary what exists, how it is held, which recovery standard applies, and where the separate recovery components are located.
It still does not contain enough secret material to spend the assets.
Layer 3: Recovery secrets
These include the seed phrase, cryptographic shares, passphrase, and signing keys.
They are kept offline and separate from the will and the complete asset map.
What the Asset Map Should Include
| Field | What to record | Security treatment |
|---|---|---|
| Plan identifier | A unique name and version date | Not secret |
| Legal owner | Individual, trust, company, or other entity | Restricted access |
| Asset and network | For example, a particular asset on Bitcoin, Ethereum, or a specific layer-2 network | Restricted access |
| Public address | A verified receiving address or account identifier | Sensitive, but not a signing secret |
| Custody type | Exchange, hardware wallet, multisig, smart account, or software wallet | Restricted access |
| Wallet software | The application used to view and manage the account | Restricted access |
| Hardware device | Manufacturer and device family | Restricted access |
| Backup standard and signing setup | BIP39, SLIP39, or the documented backup method for a multisig or other arrangement | Restricted access |
| Passphrase status | Whether a passphrase exists, but not its contents | Highly sensitive |
| Account details | Account number, script type, derivation path, or location of the wallet descriptor | Restricted access |
| Protocol positions | Staking, lending, liquidity, collateral, vesting, bridges, or governance locks | Restricted access |
| Fee requirements | The native asset needed to pay transaction fees | Restricted access |
| Tax records | Location of transaction history, acquisition records, and previous filings | Restricted access |
| Recovery contacts | Executor, attorney, technical operator, and recovery-share holders | Highly sensitive |
| Last verification | Date when access and balances were last checked | Restricted access |
Listing a token symbol is not enough.
The map must identify the network and the type of position. Where relevant, record the token’s verified contract address as well, because symbols are not unique identifiers.
A stablecoin on one network is operationally different from the same stablecoin on another network. A token deposited in a lending protocol is different from that token sitting directly in a wallet.
For each wallet, record:
- The first verified receiving address.
- The network.
- The account or wallet name.
- The wallet application.
- The backup standard.
- Whether a passphrase is used.
- Whether the wallet uses a single signer or multisig.
- Any unusual derivation path or account type.
- The location of nonsecret configuration information.
- The location and release conditions for recovery materials.
The inventory can be held in an encrypted digital document, an attorney’s secure portal, or a sealed physical packet. There should be at least two access-controlled copies.
If the inventory is encrypted, the decryption method needs its own inheritance plan. Do not protect it with the same credentials that directly control the cryptocurrency.
Also, do not assume every configuration export is nonsecret. A descriptor or export containing private keys belongs with the recovery secrets, not in the ordinary inventory.
Step 2: Set Up Threshold Recovery and a Safe Hardware Workflow
Threshold recovery can prevent one stolen document from emptying a wallet while allowing recovery when one storage location is lost.
The objective is not complexity for its own sake. It is to remove avoidable single points of failure without creating a process your family cannot execute.
Do Not Manually Cut a Seed Phrase Into Pieces
Writing the first 12 words in one place and the last 12 words somewhere else is not proper cryptographic secret sharing.
Manual splitting creates several problems:
- Each fragment exposes part of the original secret.
- There may be no redundancy.
- Losing one fragment can prevent recovery.
- The instructions may be ambiguous.
- Beneficiaries may not know the correct order.
- Depending on the phrase length and how much is exposed, partial disclosure can reduce resistance to attack.
- The split may not be compatible with wallet software.
- There is no standardized recovery procedure for your homemade arrangement.
The BIP39 specification for mnemonic-based deterministic wallets defines how a mnemonic phrase is generated and converted into seed material.
It does not define a secure method for cutting that phrase into inheritance fragments.
Use a recognized cryptographic sharing standard or a wallet’s native multisig policy instead.
Option A: Standards-Based Secret Sharing
In a properly designed secret-sharing system, a secret is divided mathematically into multiple shares. A specified minimum number is required for recovery. Fewer than the required number should not expose usable information that allows the secret to be reconstructed.
The underlying control is split knowledge. NIST’s definition of split knowledge for cryptographic keys describes a situation in which separate entities hold components that do not individually reveal the resulting key.
Its broader key-management guidance in SP 800-57 Part 1, Revision 5 addresses the protection, backup, recovery, and lifecycle management of cryptographic keying material. Those are useful operational principles, although they are not an endorsement of a particular consumer wallet.
The SLIP39 specification for Shamir-based mnemonic backups is one wallet-oriented implementation of threshold sharing.
It allows multiple word-based recovery shares and a defined recovery threshold. A 2-of-3 setup creates three shares, any two of which can restore the wallet when any required passphrase and configuration are also available. One share is insufficient.
Trezor’s explanation of Shamir backup and recovery thresholds provides a practical example of how this arrangement works on compatible hardware.
SLIP39 is different from BIP39.
A wallet that supports a standard 12- or 24-word BIP39 phrase does not necessarily support SLIP39 shares. Record the standard explicitly and verify compatibility with the hardware intended for recovery.
Common threshold arrangements include:
| Setup | Loss tolerance | Compromise threshold | Operational burden |
|---|---|---|---|
| 2-of-3 | One share can be lost | An attacker needs two shares | Low |
| 3-of-5 | Two shares can be lost | An attacker needs three shares | Moderate |
| 2-of-2 | No share can be lost | An attacker needs both shares | Fragile |
| 1-of-3 | Two copies can be lost | Any one copy permits recovery | No threshold protection |
The 1-of-3 example describes three complete recovery copies. It is not the protective multi-share arrangement people usually mean when they discuss threshold backups, and it should not be assumed to be a supported SLIP39 configuration.
For many households, I consider 2-of-3 a sensible starting point because it balances recoverability and complexity. A 3-of-5 arrangement may make sense when the portfolio and threat model justify more storage locations and participants.
Avoid a backup policy that requires every share unless there is a compelling, professionally reviewed reason.
A 3-of-3 setup may look secure, but losing one share destroys that recovery path. If no functioning device or other valid recovery route remains, the loss can become permanent.
A Practical 2-of-3 Distribution
One possible arrangement looks like this:
- Share A stays in a secure location controlled by the owner, with a documented legal path for the executor to obtain it.
- Share B is held by an attorney, professional document custodian, or another independent party under written release conditions.
- Share C is kept at a geographically separate secure location or with another trusted holder.
The locations should not be exposed to the same fire, flood, burglary, or household-level risk.
If you use a bank safe-deposit box, confirm how the executor or successor trustee can access it. Rules vary, and probate delays may make a box unsuitable as the only recovery route.
A 2-of-3 arrangement still allows any two share holders to collude. The sharing system does not know whether the owner is alive or whether recovery has been legally authorized.
For higher-risk portfolios, consider:
- A 3-of-5 threshold.
- Institutional document custody.
- Written release conditions.
- Tamper-evident packaging and inspection logs.
- Multisig custody.
- A professional fiduciary.
- A regulated custody provider for some or all of the assets, where appropriate.
Do not rely solely on share holders being unaware of one another. That may reduce opportunistic risk, but it is not a substitute for sound controls.
Label Shares Without Advertising the Portfolio
Each share should contain enough information to prevent confusion:
- The plan identifier.
- The share number.
- The recovery threshold.
- The backup standard.
- The creation date.
- Instructions never to photograph the share or enter it into a phone or ordinary computer.
It should not display:
- The owner’s complete asset inventory.
- An approximate wallet value.
- Every other storage location.
- The names of all share holders.
- The passphrase.
- A public address that exposes the portfolio.
Paper may be sufficient when held in a professionally protected environment. Durable metal can improve resistance to fire, water, and physical deterioration.
But metal improves durability, not access control.
A buried metal plate can still be stolen, forgotten, discovered during construction, damaged, or become legally inaccessible. Tamper-evident packaging is also not tamper-proof protection.
Migrating an Existing Wallet
Do not upload an existing BIP39 phrase to an online service offering to “split your seed.”
If the current wallet does not natively support the chosen threshold standard, a safer migration usually follows this sequence:
- Create a new wallet on a compatible hardware device.
- Generate the threshold shares directly on the device.
- Verify the shares.
- Send a small test amount to the new wallet.
- Restore the wallet on a second compatible device.
- Confirm that the same verified address appears.
- Send the test amount back out.
- Only then transfer the main balance.
Some devices provide documented methods for creating or changing a backup format directly on the device. If you use one, determine what happens to the old backup.
An old seed phrase may remain capable of recovering the wallet after new shares are created.
Do not destroy the old backup before the new recovery route is fully tested. Do not forget about it afterward, either. It remains a potential access route that must be controlled.
Changing the backup format does not necessarily change the underlying keys. If the old seed may have been compromised, creating new shares for the same wallet does not revoke that seed. Moving assets to genuinely new keys is a different operation.
Build a Hardware Recovery Path
Your inheritance plan should not depend on the original hardware wallet surviving.
Hardware fails. Batteries deteriorate. Screens break. Cables disappear. Firmware changes. Manufacturers stop supporting older devices.
The durable foundation is a standardized backup with the correct metadata, not the original gadget.
The plan should identify:
- A compatible hardware wallet family.
- The backup standard.
- The official software source.
- Whether recovery words are entered directly on the device.
- The account type or derivation information.
- How to verify the first receiving address.
- How to obtain a replacement device.
- How to perform a recovery rehearsal.
- What to do if the original device is damaged.
Recovery words should be entered directly into a trusted hardware device, not into an ordinary computer, browser form, phone, cloud document, or support chat.
Trezor’s instructions for handling and using a wallet backup emphasize the same practical precautions: avoid digital copies, keep the backup private, and never provide it to customer support.
For the hardware-based plan I am describing, do not create screenshots, photographs, emailed copies, or typed digital documents containing the recovery words.
Keep the active hardware wallet separate from the recovery shares. Someone who steals the device should not simultaneously obtain the materials needed to restore or bypass it.
A spare hardware device can be useful. It should not remain initialized with the live wallet unless that additional copy of the keys is deliberate and properly secured.
An uninitialized spare, or a device used for testing and then wiped, creates less lifetime exposure.
Verify the Backup Before Relying on It
An untested recovery phrase is not a verified backup. It is an assumption.
Use:
- The manufacturer’s backup-check procedure.
- A recovery test on a second compatible device.
- A separate practice wallet created through the same workflow.
A practice wallet helps validate the procedure and train participants. It does not prove that the live wallet’s actual backup was recorded correctly. The live backup still needs its own verification.
For a 2-of-3 arrangement, testing only Shares A and B leaves Share C untested. Use the manufacturer’s documented checks or a carefully supervised test plan that verifies every share.
Do not wipe the only functioning device before the recovery materials have been verified.
The backup-check and recovery troubleshooting guidance illustrates why that order matters. Verify the written materials before relying on them or performing an operation that could reset the device.
Treat Passphrases as an Advanced Feature
An optional BIP39 passphrase produces a separate wallet from the same underlying recovery phrase.
The nickname “25th word” can be misleading. A passphrase does not have to be a single word or come from the mnemonic word list. Its exact text matters, including capitalization, spaces, and punctuation.
A wrong passphrase can open a valid but entirely different wallet. The software may show an empty balance instead of an error.
If the passphrase is lost, the seed phrase alone may not recover the intended assets.
The guide to using and testing a passphrase-protected wallet makes this distinction clear: the passphrase is not something support can remove or reset.
For a nontechnical inheritance plan, I often favor a well-documented, standards-based threshold backup over adding another passphrase dependency. That judgment still depends on the wallet, assets, and threat model.
If a passphrase already exists:
- Record its existence in the asset map.
- Protect its exact contents as a separate factor.
- Do not rely on a vague hint.
- Preserve exact capitalization, punctuation, spacing, and any relevant keyboard or character-entry details.
- Test complete recovery using both the recovery phrase and the passphrase.
- Ensure the inheritance participants can obtain both components.
- Recognize that the passphrase becomes a separate single point of failure unless it also has appropriate redundancy.
SLIP39 can also use a passphrase, but its mechanism is different from BIP39. Record the actual backup standard and passphrase requirements rather than assuming the formats are interchangeable.
Option B: Multisig
Multisig, short for multiple signatures, is not the same as secret sharing.
With secret sharing, multiple shares reconstruct a single wallet recovery secret. In an ordinary single-signer wallet, that restored secret allows the necessary signing keys to be derived, concentrating control again.
With multisig, independent keys authorize transactions under a blockchain or smart-account policy. A 2-of-3 wallet requires valid approvals from two of three separate signers. The keys do not have to be combined into one master secret.
| Feature | Secret sharing | Multisig |
|---|---|---|
| What is divided? | A recovery secret | Signing authority |
| What happens during recovery or spending? | Shares reconstruct the wallet secret | Multiple keys sign independently |
| Blockchain policy | Usually appears as an ordinary single-signer wallet | A multisignature or smart-account policy |
| Main advantage | Can simplify recovery across supported assets and networks | No need to reconstruct one all-powerful recovery secret |
| Main drawback | Holders of enough shares can reconstruct the wallet | More complex configuration and coordination |
| Compatibility | Depends on the backup standard | Depends heavily on network and wallet support |
Bitcoin multisig can be highly resilient, but the individual seed phrases are not a complete backup.
The wallet may also need its full descriptor or equivalent configuration, including the cosigners’ public keys, key fingerprints, script type, threshold, and derivation information.
The BIP380 specification for output script descriptors explains why private keys alone do not tell restored software which scripts, addresses, and derivation paths to use.
A proper multisig recovery package should preserve:
- The required private-key backups.
- The complete public-only wallet descriptor or equivalent cosigner configuration.
- The threshold and script type.
- Key-origin information and fingerprints.
- The relevant receiving and change-address derivation information.
A beneficiary with two of three seed phrases but no correct multisig configuration may be unable to locate or spend the funds.
Also, descriptors can contain private keys. Keep public-only descriptor exports in the restricted configuration records. Any export containing private keys must be protected as secret recovery material.
Smart-contract multisig and social-recovery wallets can support inheritance policies on programmable networks. They also add dependencies on contracts, upgrades, guardians, relayers, and applications.
Use them only when the family has a documented support path and the relevant contracts have been widely reviewed and appropriately audited. An audit reduces uncertainty; it does not guarantee safety.
For a nondeveloper holding assets across several networks, standardized hardware recovery shares may be simpler.
For a substantial Bitcoin-focused portfolio, professionally configured multisig may provide stronger separation of authority.
Step 3: Write a Runbook for People Who Have Never Used Crypto
A technically correct backup can still fail if the family does not know what it is, where to find it, or how to use it safely.
The instruction packet should be written for someone who has never operated a hardware wallet.
I would put emergency rules on the first page, not a lecture about cryptography.
First-Page Emergency Instructions
- Do not enter recovery words into a phone, computer, website, browser extension, email, or chat.
- Do not photograph, scan, photocopy, dictate, or read recovery words aloud.
- Do not repeatedly guess the hardware wallet PIN.
- Do not reset, wipe, or update the original device.
- Do not respond to direct messages from people offering wallet recovery.
- Do not publish information about the assets.
- Contact the named executor or successor trustee.
- Contact the named attorney and technical operator using the printed contact information.
- Do not move assets until legal authority and the destination plan have been confirmed.
- Never allow an outside technician to work alone with enough recovery material to control the wallet.
These rules address the highest-risk period: the days after a death, when beneficiaries are grieving, devices are being collected, and scammers may already be monitoring public records or obituaries.
What the Complete Runbook Should Contain
Identity and authority
- The executor’s or successor trustee’s name.
- The backup fiduciary’s name.
- The attorney’s contact information.
- The technical operator’s contact information.
- The tax professional’s contact information.
- The documents required before recovery.
- Who may approve a transfer.
Asset discovery
- The wallet and account inventory.
- Networks in use.
- Public addresses.
- Custodial providers.
- Hardware devices.
- Protocol positions.
- Staking or lockup details.
- Outstanding collateralized debts.
- The location of tax and transaction records.
Recovery architecture
- The backup standard.
- The number of shares.
- The recovery threshold.
- Share locations.
- Release conditions.
- Compatible hardware.
- Whether a passphrase exists.
- The location of any multisig descriptor.
- The location of any smart-account configuration.
Destination policy
- Whether assets should be transferred in kind, liquidated, or moved into professional custody.
- Who may approve a destination address.
- Whether an estate or trust account must be opened.
- Whether a beneficiary must create a new hardware wallet.
- How minors, trusts, or beneficiaries with special needs are handled.
- How much discretion the fiduciary has during market volatility.
Transaction procedure
- How the destination address is verified.
- Which network must be used.
- Whether a memo or destination tag is required.
- Which native asset pays the network fees.
- The maximum permitted test-transfer amount.
- How long to wait before sending the remaining balance.
- Which records must be retained.
Security procedure
- Phones and cameras stay outside the recovery room.
- No remote-access software is used.
- No screen sharing is allowed.
- Sponsored search results are not used to find wallet software or support.
- The seed is not imported into a software wallet unless a specifically documented, professionally reviewed exception requires it.
- At least two people attend recovery and transfer.
- Destination addresses are independently verified.
- A written transaction log is maintained.
The runbook should use plain language.
Do not write, “Restore the HD wallet and sweep all UTXOs.”
Write the exact actions the executor will see on the screen, identify who must be present, and state when the process must stop for professional review.
Name a Technical Operator, but Limit the Operator’s Authority
A technical operator can help the executor:
- Identify appropriate hardware.
- Install official wallet software.
- Confirm the backup standard.
- Restore the wallet on a secure device.
- Locate accounts and networks.
- Prepare unsigned transaction information.
- Verify network-fee requirements.
- Record transaction identifiers.
The operator should not:
- Take recovery shares home.
- Photograph the shares.
- Work alone with the restored wallet.
- Choose beneficiaries.
- Decide whether assets should be liquidated.
- Substitute a personal address for the approved destination.
- Keep an initialized device after the process is complete.
- Require payment to an unverified address.
The fiduciary remains the legal decision-maker. The operator is a technical assistant whose work must be controlled.
This is another lesson I carry over from banking: technical competence does not automatically confer decision-making authority.
Rehearse the Plan
An inheritance plan should be tested at three levels.
Document review
Confirm that names, phone numbers, storage locations, wallet applications, addresses, and device details are current.
Tabletop rehearsal
The owner, fiduciary, and technical operator walk through the procedure without assembling enough recovery shares to meet the threshold.
Technical recovery test
Using compatible hardware, verify that the required shares restore the expected first receiving address and allow access to a small test balance.
The first matching address is an important check. It does not replace a complete inventory of every relevant account, network, passphrase wallet, and protocol position.
Review the plan after:
- Changing hardware wallets.
- Moving to a new address.
- Creating a new seed.
- Adding a passphrase.
- Changing the recovery threshold.
- Opening or closing an exchange account.
- Entering a new staking or DeFi position.
- Changing the executor, trustee, attorney, or beneficiaries.
- Moving a share to a new location.
- A significant change in wallet software.
Every packet should carry a version number and last-review date.
Retire outdated instruction copies or clearly mark them as superseded so beneficiaries do not follow conflicting procedures. Changes involving legal documents should be handled with the attorney’s guidance.
Step 4: Carry Out a Controlled Transfer or Liquidation
After recovery, the estate should move assets through an authorized, documented process, usually to fresh keys rather than keeping the deceased owner’s wallet in permanent use.
Once recovery materials have been assembled and several people have participated, I treat the original wallet as potentially exposed.
That does not mean anyone has acted dishonestly. It means the security perimeter has expanded.
The estate should restore a smaller, clearly defined perimeter through a controlled transfer.
1. Confirm Legal Authority
Before moving assets, establish who is legally authorized to act.
Depending on the structure, that may be:
- A court-appointed executor or personal representative.
- A successor trustee.
- Another authorized fiduciary.
- A person acting under the jurisdiction’s small-estate procedures.
Possessing a seed phrase does not, by itself, authorize someone to distribute estate property.
An executor or trustee may owe duties to creditors, tax authorities, beneficiaries, and the court. Technical access does not cancel those obligations.
2. Secure the Physical Materials
Collect and protect:
- Hardware wallets.
- Recovery-share envelopes.
- Computers and phones.
- Printed wallet records.
- Exchange statements.
- Password-manager instructions.
- Tax documents.
- Multisig descriptors.
- Smart-account records.
Do not casually power on, update, or reset the original hardware before understanding the state of the backups.
Preserve devices and records carefully. If their condition or security is uncertain, get qualified help before experimenting.
3. Inventory and Document the Estate’s Holdings
Before transferring assets, record:
- The date and time.
- Wallet addresses.
- Asset types and quantities.
- Networks.
- Relevant protocol positions.
- Outstanding debt or collateral.
- Staking rewards not yet received.
- Transaction history.
- Available cost-basis information.
- Acquisition records.
- The valuation source selected by the tax professional.
The records may need to support a date-of-death valuation as well as later transactions. Preserve the relevant dates, timestamps, and valuation methodology.
The IRS guidance on digital-asset reporting and recordkeeping explains that taxpayers must retain records sufficient to support the information reported on their returns. Those records can include receipts, sales, exchanges, dispositions, transfers, fair market value, and basis.
Do not assume an exchange or blockchain explorer will provide a complete cost-basis history.
Preserve the deceased owner’s original transaction files, exchange exports, wallet histories, and previous tax documentation.
Also, do not assume the beneficiary automatically takes over the owner’s historical cost basis unchanged. Applicable inheritance and valuation rules may affect basis, while post-death income, rewards, and later sales may require separate treatment. A qualified tax professional should determine the correct approach.
4. Prepare the Destination Before Restoring the Wallet
Establish and independently verify the destination before bringing the recovery shares together.
Possible destinations include:
- A temporary wallet controlled by the estate or trust.
- A regulated custody account opened for the estate or trust.
- A new hardware wallet controlled by the beneficiary.
- An authorized exchange account used for liquidation.
- A professionally administered multisig arrangement.
Where a new self-custody wallet is used, it should have genuinely new keys and its own verified backup. A different address derived from the deceased owner’s old seed is not a new security boundary.
Confirm the destination address on the receiving hardware device’s display or through another trusted verification method.
Two people should compare the complete address, network, and any required memo or destination tag.
Do not rely on an address copied from an email. Clipboard malware and compromised messaging accounts can substitute an attacker’s address.
5. Restore Under Two-Person Control
Use:
- A private room without active cameras.
- A trusted, fully updated computer without unnecessary software.
- Official wallet software obtained from a verified source.
- A new or trusted hardware device.
- The smallest necessary group of authorized participants.
- A written event log.
Keep phones outside the room. Cover built-in cameras and disable microphones where necessary.
Follow the manufacturer’s process to update an empty replacement device before entering recovery material. If using the original device, avoid firmware changes until the backup has been verified.
Enter recovery words directly on the hardware device.
During the documented setup and recovery workflow:
- Set a fresh device PIN.
- Open the documented wallet application.
- Enable the required networks.
- Confirm the expected first receiving address.
- Compare balances with the relevant blockchain records.
- Resolve discrepancies before signing anything.
If the expected address does not appear, stop.
Possible explanations include:
- The wrong passphrase.
- The wrong backup.
- A different account number.
- A different derivation path.
- An unsupported network.
- Missing multisig configuration.
- The wrong wallet application.
- An undiscovered smart account or protocol position.
Do not randomly try settings while the full recovery secret is exposed.
The correct response to an unexplained mismatch is a controlled pause, not more improvisation.
6. Send a Test Transaction
For each relevant network:
- Verify the destination address on the receiving hardware device or through the approved custody-verification process.
- Confirm the network.
- Confirm whether a memo or destination tag is required.
- Retain enough native currency for network fees.
- Send a small test amount.
- Wait for the appropriate confirmations or finality.
- Confirm receipt from the destination side.
- Record the transaction identifier.
If the destination is an exchange or custodian, the test must also satisfy its minimum-deposit requirements. A transaction appearing on-chain is not the same as the provider crediting the correct account.
A successful test on one network does not prove that another network, another token, or another custody arrangement is configured correctly.
Do not send away all the native fee asset before moving the tokens and positions that still require it.
During inheritance administration, avoid unnecessary bridges, swaps, contract interactions, and wallet imports. Every additional action introduces another possible failure and another event that may need tax documentation, even if the action is not itself taxable.
7. Transfer, Liquidate, or Move Into Professional Custody
The estate plan should express the owner’s wishes while giving the fiduciary enough lawful discretion to respond to:
- Volatility.
- Market liquidity.
- Network congestion.
- Exchange restrictions.
- The beneficiary’s ability to maintain secure custody.
- Tax requirements.
- Custody risks.
- Court deadlines.
- Protocol lockups.
- Emergency security circumstances.
| Distribution method | Main advantage | Main trade-off |
|---|---|---|
| Transfer in kind | Preserves the assets themselves and avoids forcing a market sale at a particular time | The beneficiary must manage custody securely |
| Liquidation | Simplifies distribution and estate accounting | Introduces market, fee, timing, and tax considerations |
| Professional custody | Reduces the beneficiary’s key-management responsibilities | Adds fees, provider risk, and account-opening requirements |
| Hybrid approach | Balances liquidity needs with continued asset exposure | Requires more decisions and documentation |
For an in-kind transfer, the beneficiary should receive the assets into a newly created wallet with fresh keys.
The deceased owner’s recovered wallet should not become the beneficiary’s permanent wallet.
For liquidation, the fiduciary should use a properly authorized estate or trust account where possible, rather than route assets through a beneficiary’s personal exchange account.
For professional custody, the fiduciary should verify:
- The legal owner of the account.
- Withdrawal rules.
- Beneficiary or successor-authority arrangements.
- Insurance claims, coverage terms, and exclusions.
- Supported assets and networks.
- Fees.
- Geographic restrictions.
- Recordkeeping capabilities.
Do not assume that marketing language about custody or insurance provides the same protection as a traditional insured bank deposit. Verify exactly what is covered and under what conditions.
8. Close Out the Recovery Process
After all authorized transfers:
- Retain transaction identifiers.
- Retain exchange trade confirmations.
- Record network and service fees.
- Reconcile final balances.
- Monitor old addresses for later incoming payments.
- Retain watch-only access when useful.
- Wipe temporary recovery devices that will not remain in use.
- Return unused secret shares to controlled storage.
- Preserve original recovery materials until the fiduciary and attorney confirm that no additional assets, refunds, rewards, or claims remain.
- Document any eventual destruction of obsolete recovery materials.
Do not destroy a signing path while a locked position, delayed reward, refund, or other legitimate claim may still require it.
The recovered wallet should be treated as potentially compromised after the process, even when every participant is trusted. More people have observed the workflow, devices have been connected, and recovery shares have been brought together.
Moving to fresh keys reestablishes a smaller security perimeter.
How to Choose the Right Crypto Inheritance Architecture
The safest inheritance architecture is the simplest one that adequately addresses the portfolio’s value, complexity, and risks.
More moving parts do not automatically mean better security. Complexity is itself a source of loss.
| Portfolio type | Reasonable starting architecture | Main warning |
|---|---|---|
| Small, straightforward holdings | Hardware wallet, verified backup, restricted inventory, and clear executor instructions | A single physical backup remains a point of failure |
| Meaningful portfolio across multiple networks | Hardware wallet with documented, standards-based 2-of-3 recovery shares | Verify support for every relevant wallet and network |
| Large Bitcoin-focused portfolio | Professionally reviewed 2-of-3 multisig with complete descriptor backups | Configuration information matters as much as seed backups |
| Complex estate with staking or DeFi positions | Formal fiduciary structure, specialized runbook, and professional support | A seed phrase alone may not explain how to unwind positions |
| Owner with nontechnical beneficiaries | Planned transfer into professional custody or supervised liquidation | Provider selection and account-opening delays require advance planning |
| Business or institutional treasury | Governance policies, multiple signers, documented succession, and activity logs | Consumer seed-storage methods may be inadequate |
For a wallet worth a few hundred USD or EUR, an expensive institutional arrangement may be disproportionate.
A simple, tested hardware backup and a precise instruction packet may be safer than an elaborate scheme nobody rehearses.
As portfolio value increases, the cost of professional legal review, independent key storage, multisig, or professional custody becomes easier to justify.
Value is not the only factor, though.
A modest wallet spread across several networks, smart contracts, and staking systems may need a more detailed plan than a much larger wallet holding one straightforward asset.
I assess operational complexity alongside financial value. Both influence how difficult the estate will be to administer.
Operational Costs and Trade-Offs
A sound crypto inheritance plan has both financial costs and ongoing administrative responsibilities.
The initial setup is only part of the expense. The plan also has to remain accurate and executable.
| Component | Cost pattern | What it provides | Main trade-off |
|---|---|---|---|
| Estate-planning attorney | Initial drafting and periodic reviews | Valid authority and jurisdiction-appropriate documents | Professional fees |
| Additional hardware wallet | One-time equipment cost | Recovery testing and a safer transfer process | Another device to manage |
| Durable backup material | One-time physical cost | Resistance to fire, water, and deterioration | Does not prevent theft |
| Secure storage | One-time or recurring cost | Physical separation and access control | Access delays and dependence on the storage provider |
| Professional fiduciary | Setup costs and recurring fees | Neutral administration and continuity | Institutional cost and trust requirements |
| Multisig coordinator or custody provider | Setup, recurring, or transaction-based fees | Policy enforcement and technical support | Provider and compatibility dependencies |
| Network fees | Per-transaction cost | Moving assets on-chain | Can be unpredictable |
| Exchange costs | Trading fees, spreads, and withdrawal fees | Liquidation and fiat distribution | Market and counterparty exposure |
| Rehearsal time | Recurring administrative effort | Evidence that the plan works | Requires discipline |
| Tax preparation | Professional cost when relevant events occur | Support for basis, valuation, and reporting | Can become expensive when records are poor |
The hidden cost I pay the most attention to is maintenance.
A plan becomes dangerous when it describes a wallet, device, attorney, or storage location that no longer exists.
A good system minimizes dependencies while preserving enough redundancy to survive an ordinary failure or loss.
Common Crypto Inheritance Mistakes
Putting a Seed Phrase in a Will
This can turn a probate record into a theft mechanism.
The will should establish authority, not contain credentials that allow whoever possesses them to control the assets.
Giving One Beneficiary the Complete Seed in Advance
This simplifies inheritance by sacrificing lifetime security.
The beneficiary’s phone, home, relationships, and financial pressures become part of the owner’s threat model.
Trusting someone personally is not the same as knowing that every device, account, and physical location around that person is secure.
Splitting a BIP39 Phrase Into Groups of Words
This is not standards-based secret sharing.
It creates ambiguity, weakens redundancy, and can produce a recovery arrangement that fails when one fragment disappears.
Storing Every Share in the Same Building
Three envelopes in one home are exposed to the same fire, flood, burglary, or accidental disposal.
Separate shares need genuinely independent storage locations, not merely different drawers.
Requiring Every Share
A 3-of-3 backup has no loss tolerance.
One missing envelope can destroy the recovery path. If no other valid access remains, the wallet can become permanently inaccessible.
Keeping the Device and Backup Together
A stolen safe, bag, or document box may give an attacker both the hardware and the means to restore the wallet.
Physical convenience can erase the separation your security design was supposed to create.
Treating the Hardware PIN as an Inheritance Plan
A PIN may provide access to the current working device.
It cannot restore a broken, wiped, or obsolete device. It is not a substitute for a verified backup and the required configuration.
Forgetting the Passphrase
The correct recovery phrase without the intended passphrase may open the standard wallet or another wallet rather than the one holding the assets.
Every required character must be preserved and tested.
Backing Up Multisig Seeds Without the Configuration
Multisig recovery may also require the descriptor, cosigner public keys, threshold, script type, fingerprints, and derivation information.
The seeds and the wallet policy are separate parts of the recovery package.
Keeping the Master Seed in Email or Ordinary Cloud Storage
Encryption may reduce some risks, but it introduces dependencies involving account recovery, the provider, malware, credentials, and the decryption key.
A nontechnical beneficiary should not have to master an improvised digital-security system before being able to use the hardware-security system.
Using an Automated Switch to Release the Key
Inactivity is not death.
False triggers and failures to trigger remain possible when the system lacks a reliable process for establishing that the owner has died.
Failing to Identify the Network
A token name alone does not tell the executor where the asset is held or which native currency is needed for fees.
It also does not identify whether the asset is directly held, bridged, staked, or deposited in a protocol.
Ignoring Staking, Lending, and Collateral
A visible wallet balance may not show assets deposited in a protocol, locked in a contract, delegated, or pledged against debt.
The estate may need to manage an unbonding period, repay a loan, or close a position before distribution is possible.
Moving Everything Without a Test Transaction
Blockchain transfers are generally irreversible.
A small test can reveal the wrong network, address, memo, wallet, or custody configuration before the entire estate is placed at risk.
Letting an Online “Recovery Expert” Work Alone
A technician who sees the complete seed can recreate the wallet later.
Recovery should use two-person control and direct entry on trusted hardware, followed by an authorized transfer to fresh keys.
Nobody should receive unsupervised control merely because they know more technical terminology than the family.
Failing to Update the Plan
A perfect plan for a wallet emptied three years ago is useless.
Every wallet migration should trigger an inheritance-plan review.
Crypto Inheritance Checklist for the Owner
Use this checklist to turn the protocol into an operating plan rather than a document your family hopes will work.
- Identify the executor, successor trustee, backup fiduciary, and beneficiaries.
- Name a technical operator who can assist without taking over legal decisions.
- Ask a local attorney to address authority for digital-asset access, management, professional assistance, transfer, and liquidation.
- Remove every private key, seed phrase, passphrase, and PIN from the will.
- Build a complete inventory by network, address, wallet, custody type, and protocol position.
- Record wallet software, hardware family, backup standard, and account configuration.
- Decide whether the current wallet should remain single-signer, use secret sharing, or move to multisig.
- If using recovery shares, choose a loss-tolerant threshold such as 2-of-3 or 3-of-5.
- Generate shares through a documented hardware workflow or standardized system.
- Store shares at independent physical locations.
- Document how the executor can legally obtain the required number of shares.
- Keep the active device separate from recovery materials.
- Test recovery on compatible hardware.
- Verify the expected first receiving address.
- Fund and spend a small test amount before moving the main portfolio.
- Write a first-page emergency checklist for nontechnical beneficiaries.
- Document the destination, test-transfer, and two-person verification procedures.
- Preserve acquisition, transaction, valuation, and tax records.
- Conduct a tabletop rehearsal.
- Put a date and version number on every copy of the plan.
- Review the plan after any significant wallet, legal, family, or custody change.
- Schedule a regular review even when nothing appears to have changed.
The Core Principle: Separate Authority, Recovery, and Transfer
Crypto inheritance should depend on a controlled process that authorized people can carry out, not on publishing a private key after death.
The will or trust answers who has authority.
The asset map answers what exists.
The recovery design, including a threshold arrangement where appropriate, answers how access can be restored without relying on one vulnerable master copy.
The beneficiary runbook answers which actions happen, in what order, and under whose supervision.
The transfer procedure answers where the assets go and how the estate documents the result.
That separation is what conventional estate planning can miss when it treats cryptocurrency like an ordinary financial account.
A legal document without key recovery can create ownership without access.
A seed phrase without legal instructions can create access without authority.
My approach is to connect those two sides while keeping the secrets out of probate files, cloud timers, and improvised family procedures.
The goal is not to turn your heirs into crypto experts. It is to leave them a plan they can follow safely, lawfully, and without guessing.
Sponsored Partner: Volet.com
Looking for a simple, everyday way to buy, hold, and sell cryptocurrencies alongside your traditional currencies and payment cards?
- Read my full breakdown: Complete Volet Review on DoraMilen.com
- Get started right away: Open your free Volet account using my referral link