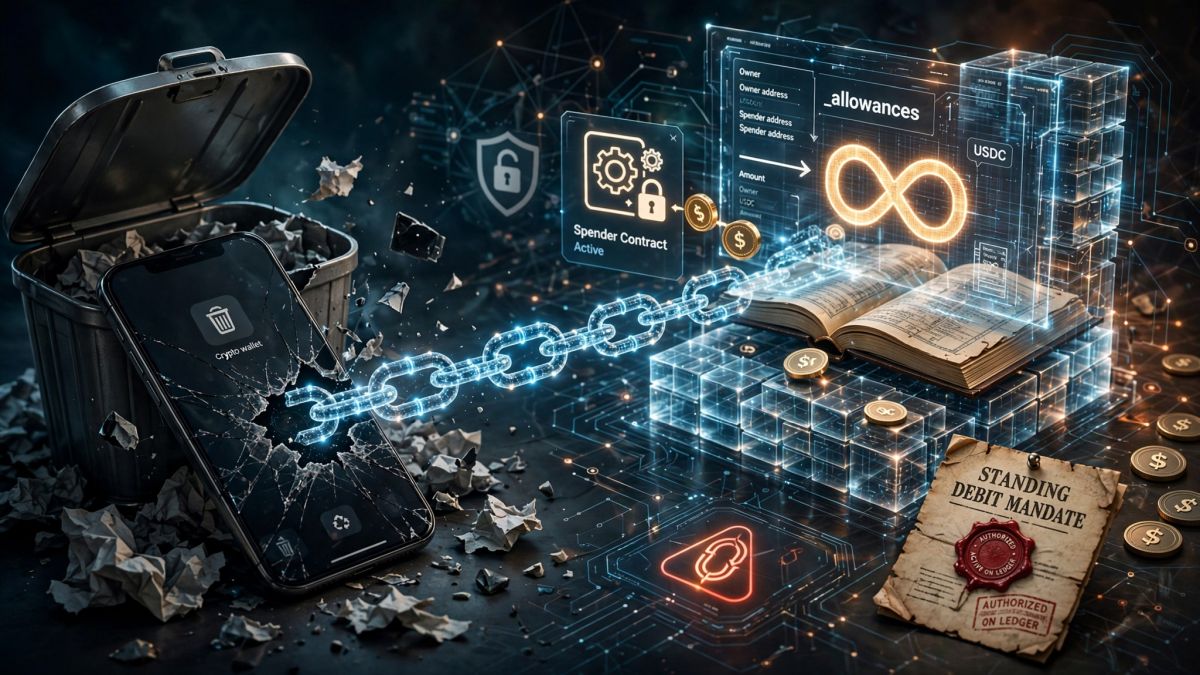
Deleting a crypto wallet app from your phone or clicking “Disconnect” on a decentralized application website does not cancel the smart contract permissions you previously signed, because token approvals live permanently on the blockchain ledger rather than on your mobile device.
After 25 years in traditional banking, I have watched hundreds of retail and corporate clients make the exact same conceptual mistake with Automated Clearing House (ACH) standing debit authorizations. A client would sign a standing debit mandate allowing a vendor or utility company to pull funds directly from their checking account every month. Months later, after a dispute with the vendor, the client would shred their paper copy of the contract, throw away the pen they signed it with, or delete their mobile banking app from their phone, assuming the vendor was now locked out. Then they would call my desk in a panic when another debit cleared their account.
I always had to explain the same fundamental rule of financial clearing: throwing away the pen you used to sign a power of attorney does not revoke the power of attorney. The authorization does not live inside your pen, and it does not live inside the app on your phone. It sits on the clearing ledger at the settlement institution.
In Web3, that settlement ledger is the blockchain, and the standing debit mandate is called a token approval. When you interact with a decentralized exchange (DEX), lending protocol, bridge, or NFT marketplace, you sign an on-chain authorization allowing that protocol’s smart contract to pull specific tokens straight out of your wallet. According to Scam Sniffer’s 2025 crypto phishing report, wallet-drainer phishing stole USD 83.85 million across Ethereum Virtual Machine (EVM) chains in 2025 alone, with many victims losing funds through dormant, unlimited approvals sitting quietly in their wallets long after they stopped using an application.
If you have ever deleted a wallet app, removed a browser extension, or clicked “Disconnect Wallet” after hearing about a protocol exploit, your assets may still be completely exposed. Here is how token approvals actually work under the hood, why local device actions do nothing to protect your balances, and how I execute a six-month permission audit to keep my own wallets locked down.
Token Approvals Explained Simple: How the Two-Step Pull Pattern Works
A token approval is an on-chain permission recorded inside a token smart contract that authorizes a specific third-party contract address, known as the spender, to withdraw up to a designated amount of tokens from your wallet without requiring a new signature for every transfer.
When I look at how legacy clearing systems handle payments versus Ethereum, the distinction comes down to “push” versus “pull” settlement. When you send native ETH or Bitcoin from your wallet to a friend, you are initiating a push payment, much like a Fedwire transfer. You specify the recipient, sign the instruction, and push the asset out of your custody.
However, ERC-20 tokens (like USDC, USDT, UNI, or WETH) are not native protocol assets. Each ERC-20 token is actually an independent database living inside its own smart contract. Because of how the original ERC-20 standard was designed, an ERC-20 token cannot simply “push” itself into a decentralized exchange contract and automatically trigger a swap in a single step. If you transfer USDC directly to a Uniswap router contract using a standard transfer function, the router contract is never notified that the funds arrived, and your tokens get stuck inside the contract.
To solve this, DeFi protocols rely on a two-step pull pattern, as detailed in Jumpstart Blockchain’s technical breakdown of ERC-20 allowances. Instead of pushing tokens to the dapp, you instruct the token contract to let the dapp pull them:
- Step 1 (The Authorization): You submit an on-chain transaction calling
approve(address spender, uint256 amount)on the token contract itself. No tokens move during this step. Instead, the token contract updates its internal double-entry accounting ledger to record that thespendercontract is allowed to withdraw up toamountfrom yourowneraddress. - Step 2 (The Execution): You initiate the actual swap, deposit, or bridge transaction on the dapp. During that transaction, the dapp’s smart contract calls
transferFrom(address from, address to, uint256 amount)on the token contract. - Step 3 (The Ledger Check): The token contract checks its internal
allowancemapping. If the requested amount is less than or equal to the remaining allowance you granted in Step 1, the token contract moves the tokens from your wallet to the protocol and deducts that amount from your remaining allowance.
Under the hood, every standard ERC-20 token contract maintains two core state mappings in EVM storage:
// Stores the actual token balance of each wallet address
mapping(address => uint256) private _balances;

// Stores the spending cap: Owner Address => (Spender Address => Allowed Amount)
mapping(address => mapping(address => uint256)) private _allowances;
Notice what is stored in that second mapping: an owner address, a spender address, and a numeric cap. As highlighted in BTC Pulse’s analysis of token allowances, the token contract does not know or care whether your phone is turned on, whether your browser extension is connected to a website, or why the spender contract is pulling the funds. As long as _allowances[yourWallet][spenderContract] is greater than zero, the spender contract has unilateral authority to call transferFrom and pull your tokens.
Why Deleting an App or Clicking ‘Disconnect’ Does Not Revoke Access
Disconnecting your wallet from a website or uninstalling a crypto app from your phone only terminates the local front-end communication session on your device, leaving all on-chain smart contract allowances active and executable.
One of the most dangerous misconceptions in retail crypto comes from Web2 muscle memory. On an iPhone or Android device, if you delete an app or revoke its camera permission in your operating system settings, that app can no longer access your camera. The operating system acts as an active gatekeeper between the software and your hardware.
In Web3, your mobile wallet app (such as MetaMask, Trust Wallet, Coinbase Wallet, or Rainbow) is not a vault that holds your coins, and it is not a gatekeeper that blocks smart contracts from executing. Your wallet app is merely a local key-signing interface and a blockchain browser.
When you visit a dapp and click “Connect Wallet,” you are establishing a front-end session (via an injected browser provider or WalletConnect). That connection simply lets the website read your public wallet address and send transaction requests to your screen. As explained in MetaMask’s official guidance on disconnecting from a dapp, disconnecting your wallet only closes that front-end window so the website stops seeing your address or prompting you in that browser session.
Similarly, Ethereum’s official guide to revoking token access emphasizes that on-chain permissions remain live indefinitely until you broadcast a new blockchain transaction to overwrite them. Let us compare what actually happens across the technical stack when you take different security actions:
| User Action | Technical Layer Affected | Network Gas Cost | Effect on Active Token Allowances | Protects Against Compromised Spender Contract |
|---|---|---|---|---|
| Delete wallet app from phone | Local device storage only | Free | None (allowances remain 100% active on-chain) | No |
| Click Disconnect Wallet on a dapp | Browser session / WalletConnect relay | Free | None (allowances remain 100% active on-chain) | No |
| Lock hardware wallet in a safe | Local private key signing hardware | Free | None (existing allowances do not need a new signature) | No |
Revoke approval (approve set to 0) | Blockchain state (_allowances mapping) | Costs gas in native token | Resets specific spender cap to zero for that token | Yes (for that specific token and spender) |
| Move tokens to a brand-new wallet | Blockchain state (_balances mapping) | Costs gas in native token | Old wallet still has allowances, but holds zero balance | Yes (empties the balance before spender can pull) |
Look closely at row three in that table: locking your hardware wallet in a bank vault does not protect you from an active token approval. In my conversations with high-net-worth investors, this is the point that shocks them the most. They assume that because their Ledger or Trezor is unplugged and locked away, no tokens can ever leave their address without a physical button press.
As noted in Matcha’s guide to revoking smart contract permissions and Blockready’s wallet permission safety analysis, a hardware wallet only protects your private signing key. Once you press the physical buttons on your hardware wallet to sign an approve transaction, your signature’s job is finished. When the spender contract later calls transferFrom to pull your tokens, it uses its own address to trigger the transaction, not your private key.
The Hidden Danger of Unlimited (uint256 Max) Allowances
An unlimited token approval sets your on-chain spending allowance to the maximum 256-bit unsigned integer (2^256 - 1), granting a smart contract permanent, uncapped authority to withdraw your entire current and future balance of that token.
If you only need to swap 500 USDC on a decentralized exchange, the logical banking practice would be to authorize a single debit of 500 USDC. Once the swap settles, the allowance drops to zero. As explained in MetaMask’s analysis of token approval mechanics, if you return tomorrow to swap another 500 USDC, you would have to submit a new approve transaction and pay another network gas fee.
To save users gas fees and reduce user-interface friction, most DeFi applications request an “Unlimited” approval by default on your very first interaction. In the EVM, there is no special boolean flag for “infinite.” Instead, the dapp populates the amount parameter of the approve function with the largest number a 256-bit slot can hold: 2^256 - 1.
When you inspect the raw transaction data in your wallet or on a block explorer, an unlimited approval looks like this:
Function: approve(address spender, uint256 amount)
MethodID: 0x095ea7b3
[0]: 000000000000000000000000def1c0ded9bec7f1a1670819833240f027b25eff (Spender Address)
[1]: ffffffffffffffffffffffffffffffffffffffffffffffffffffffffffffffff (Amount: uint256 max)
Converted from hexadecimal to decimal, those 64 f characters equal:
115,792,089,237,316,195,423,570,985,008,687,907,853,269,984,665,640,564,039,457,584,007,913,129,639,935Because that number is astronomical (far larger than the total supply of any legitimate token in existence), your allowance never runs out. Even when the token contract subtracts 500 USDC during a standard transferFrom call (or skips decrementing altogether as a gas optimization when it sees type(uint256).max), the remaining allowance stays effectively infinite.
As highlighted in Coinspeaker’s 2026 guide to revoking crypto permissions and Blockscout’s guide to revoking unlimited token approvals, this creates a massive, silent time bomb in your wallet architecture:
- In 2024, you connect your wallet to an experimental cross-chain bridge or yield aggregator to move 200 USDT.
- You click “Approve” on the default unlimited prompt, complete your bridge transfer, close the browser tab, and delete the mobile app.
- Two years later, in October 2026, you receive 150,000 USDT into that same wallet address from an OTC settlement or treasury distribution.
- That same week, an attacker discovers an unvalidated calldata bug in the old 2024 bridge contract (or compromises the developer’s proxy upgrade admin key).
- The attacker instructs the bridge contract to call
transferFromagainst every wallet that ever granted it an unlimited USDT allowance. Your 150,000 USDT is drained in a single block without you clicking a link, opening an app, or signing a transaction.
In traditional finance, leaving an uncapped, non-expiring debit authorization open with every counter-party you have ever done business with would get a corporate treasurer fired on the spot. As noted in BitEarnings’ review of unlimited allowance exposure, DeFi investors must treat open token allowances exactly like uncapped counterparty credit exposure.
Beyond Standard ERC-20 approve: NFT Operators, EIP-2612 permit, and Permit2
Modern Web3 permissions extend well beyond standard on-chain ERC-20 approve calls to include collection-wide NFT operator permissions (setApprovalForAll), off-chain EIP-2612 permit signatures, and Uniswap’s Permit2 middleware contract.
If you only look for classic ERC-20 approve transactions when auditing your wallet, you will miss three major permission vectors that attackers actively exploit.
1. ERC-721 and ERC-1155 setApprovalForAll
Non-fungible tokens (NFTs) use different contract functions than fungible tokens. While ERC-721 includes a single-item approve(address to, uint256 tokenId) function, most NFT marketplaces (such as OpenSea or Blur) ask you to call setApprovalForAll(address operator, bool approved) instead. As explained in Zerion’s overview of token allowances and Bitrue’s wallet protection overview, setting approved to true gives that operator contract blanket authority to transfer every single NFT you hold within that specific collection contract, including new NFTs from that collection that you buy months later.
2. EIP-2612 Gasless permit Signatures
Standard ERC-20 approvals require you to pay gas and submit an on-chain transaction before you can trade. To eliminate this friction, Coinpaper’s overview of Revoke.cash notes that EIP-2612 introduced the permit extension. With EIP-2612, you do not submit an on-chain transaction to grant an allowance. Instead, your wallet prompts you to sign an off-chain EIP-712 typed data message containing these exact parameters:
{
  "types": {
    "Permit": [
      { "name": "owner", "type": "address" },
      { "name": "spender", "type": "address" },
      { "name": "value", "type": "uint256" },
      { "name": "nonce", "type": "uint256" },
      { "name": "deadline", "type": "uint256" }
    ]
  },
  "primaryType": "Permit",
  "domain": {
    "name": "USD Coin",
    "version": "2",
    "chainId": 1,
    "verifyingContract": "0xA0b86991c6218b36c1d19D4a2e9Eb0cE3606eB48"
  },
  "message": {
    "owner": "0xYourWalletAddress...",
    "spender": "0xSpenderContractAddress...",
    "value": "115792089237316195423570985008687907853269984665640564039457584007913129639935",
    "nonce": 0,
    "deadline": 1999999999
  }
}
Why is this so dangerous in phishing attacks? Because signing an off-chain message costs zero gas and feels harmless to casual users who think they are just “logging in” or “verifying ownership.” Once you hand that cryptographic signature (v, r, s) to a phishing website, the attacker takes your signed message, submits it to the token contract’s permit() function on-chain, pays the gas fee themselves, sets your allowance to unlimited, and immediately calls transferFrom to empty your balance.
3. Uniswap’s Permit2 Middleware Layer
Because many older tokens (like mainnet USDT or WETH) never implemented EIP-2612, Uniswap Labs introduced Permit2, which is now widely used across DEX aggregators like Matcha and 1inch. As explained in NOWNodes’ technical guide on EIP-2612 and Permit2 allowances, Permit2 splits permissions into two layers:
- Layer 1 (Traditional ERC-20 Allowance): You grant a standard on-chain
approve(usually unlimited) to the canonical, non-upgradablePermit2smart contract (0x000000000022D473030F116dDEE9F6B43aC78BA3). - Layer 2 (Signature or Allowance Transfer inside
Permit2): Whenever you trade on a dapp that integratesPermit2, you sign a time-bounded message authorizing that specific dapp to pull tokens through yourPermit2allowance until an expiration timestamp.
While Permit2 improves security for honest dapps by enforcing expiration timestamps on Layer 2, phishing kits quickly adapted. Because millions of users already have an active Layer 1 unlimited approval pointing to the Permit2 contract, drainers now trick victims into signing a malicious PermitSingle or PermitBatch off-chain message that names the attacker’s address as the Layer 2 spender. If you suspect you signed a suspicious Permit2 message before the attacker broadcast it, you must either invalidate your Permit2 nonce or revoke your Layer 1 token approval to the Permit2 contract itself.
Protocol Quirks: The approve Race Condition and Mainnet USDT
Modifying an existing non-zero ERC-20 allowance directly exposes users to a mempool front-running race condition, which is why legacy contracts like Ethereum mainnet USDT strictly revert unless the allowance is set to zero first.
When you examine how ERC-20 contracts behave in production, not all tokens follow the standard specification cleanly. As documented in Jumpstart Blockchain’s smart contract security guide, the standard approve function suffers from a well-known ordering flaw:
- Suppose you previously approved a spender contract for
100 USDC, and you want to reduce that limit to50 USDC. - You submit a transaction calling
approve(spender, 50). - A malicious spender monitoring the public mempool sees your pending transaction. It immediately broadcasts a
transferFromtransaction with a higher priority gas fee to pull the full100 USDCbefore your transaction is included in a block. - Your
approve(spender, 50)transaction then executes, overwriting the allowance to50 USDC. - The spender immediately calls
transferFroma second time to pull the new50 USDC, stealing150 USDCtotal when you only ever intended to risk100and then50.
Because of this race condition, Ethereum mainnet’s Tether (USDT) contract (0xdAC17F958D2ee523a2206206994597C13D831ec7) enforces a strict check directly in its Solidity code: if your current allowance is non-zero (for example, 100) and you call approve(spender, 50), the transaction will revert and fail. You are forced to call approve(spender, 0) first, wait for confirmation, and then set the new non-zero amount. In addition, mainnet USDT violates the ERC-20 standard by not returning a bool value from approve().
As noted in CryptoTimes’ comparison of EVM and Solana permissions, tools like Revoke.cash and Etherscan handle zero-value revocations automatically because setting an allowance to 0 is always permitted by USDT. However, if you are writing smart contracts that manage allowances programmatically (especially since OpenZeppelin v5 removed the legacy increaseAllowance and decreaseAllowance helpers), you should always use OpenZeppelin’s SafeERC20 library and its forceApprove method:
// SPDX-License-Identifier: MIT
pragma solidity ^0.8.20;

import {IERC20} from "@openzeppelin/contracts/token/ERC20/IERC20.sol";
import {SafeERC20} from "@openzeppelin/contracts/token/ERC20/utils/SafeERC20.sol";

contract TreasuryManager {
    using SafeERC20 for IERC20;

    function updateRouterAllowance(address token, address router, uint256 newAmount) external {
        // forceApprove automatically handles tokens that do not return a bool (like USDT)
        // and resets the allowance to 0 first if a direct non-zero change reverts.
        IERC20(token).forceApprove(router, newAmount);
    }
}
It is also worth noting that non-EVM chains handle permissions differently. On Solana, for instance, tokens do not sit inside a single monolithic ERC-20 mapping. Instead, every SPL token you hold lives inside its own dedicated Associated Token Account (ATA) controlled by your wallet, where permissions are granted by assigning a single delegate authority to that specific token account rather than an open-ended mapping of dozens of spenders.
How to Revoke Crypto Permissions After a Hack (Emergency Triage Protocol)
If you suspect a protocol exploit or realize you just signed a malicious approval, your immediate priority is transferring your remaining liquid tokens to a clean, uncompromised wallet before broadcasting on-chain revocation transactions to set exposed allowances to zero.
When panic sets in after a phishing click or a breaking news alert about a DeFi protocol hack, most users make costly tactical errors. Based on ByPanther’s multi-chain revocation guide and CryptumPay’s wallet permission security guide, here is the exact incident-response sequence I use when triaging an exposed wallet:
- Step 1 (Distinguish Seed Phrase Compromise from Approval Exploit): Before you send any gas to the affected wallet, determine what was actually compromised. If your native gas token (like ETH, BNB, or POL) is being swept out of the wallet the exact second it arrives, an attacker has your seed phrase or private key and is running an automated sweeper bot. Revoking token approvals will not fix a leaked seed phrase, because anyone holding the private key can simply sign new transactions. If only a specific ERC-20 token or NFT collection moved (or if you only signed an
approve/permitprompt without typing your 12-word recovery phrase anywhere), you are dealing with an approval issue. - Step 2 (Evacuate High-Value Tokens to a Fresh Wallet First): Suppose you hold 50,000 USDC in your wallet and realize you just granted an unlimited USDC allowance to a suspicious contract, but the drainer has not pulled the funds yet. Do not start by revoking the approval. Both transferring your USDC to a clean wallet and revoking the approval require one on-chain transaction. If you submit a
revoketransaction first and a mempool bot spots it, the drainer can front-run your revocation. If you transfer the 50,000 USDC out to a clean wallet first, the balance drops to zero immediately, removing the prize. - Step 3 (Revoke Exposed Allowances by Setting Them to Zero): Once your liquid balances are safe (or if your tokens are locked in staking/vesting and cannot be moved), connect to a trusted approval checker or use the CLI to broadcast
approve(spender, 0)for every compromised or unknown spender. - Step 4 (Verify On-Chain State): Never trust a front-end confirmation pop-up alone. Refresh the block explorer or query the contract state directly to verify that
allowance(owner, spender)now returns0.
As outlined in CryptoAdventure’s 2026 wallet permission safety guide, different scenarios call for specific remediation priorities:
| Security Scenario | Nature of the Threat | Immediate Recommended Action |
|---|---|---|
| You clicked a phishing link and signed a pop-up, but funds are still in wallet | Malicious approve, setApprovalForAll, or permit signature waiting to be executed | Transfer high-value tokens to a fresh wallet immediately, then sort approvals newest-to-oldest and revoke the unknown spender |
| A legitimate DeFi protocol you used 6 months ago just got hacked | Attackers can exploit the compromised router/vault to pull funds via old unlimited allowances | Check official incident reports for the affected contract address and immediately revoke allowances to that spender |
| You uninstalled a wallet app or disconnected a site after a single swap | Dormant unlimited approval remains live on the blockchain indefinitely | Open an approval checker on the specific network you used and set the unused allowance back to zero |
| You are about to deposit large funds into an old hot wallet you have not used in a year | Forgotten approvals from past experiments can immediately expose incoming token balances | Audit and clear all open ERC-20, NFT, and Permit2 allowances across all chains before sending new funds to the address |
| Native ETH and multiple unrelated tokens were drained simultaneously without new approvals | Private key or 12/24-word seed phrase compromise | Abandon the wallet permanently; do not send gas to revoke approvals, as a sweeper bot will steal the gas |
How to Inspect and Revoke Allowances Directly (CLI, Explorers, and Dashboards)
You can audit and revoke smart contract allowances through three primary methods: querying and writing directly to the blockchain via Foundry’s cast CLI, using built-in block explorer tools like Etherscan and Blockscout’s Revokescout, or connecting to multi-chain dashboards like Revoke.cash and Rabby Wallet.
Why do I insist on knowing all three methods? Because during a major DeFi security event, third-party web interfaces can go offline, suffer RPC rate-limiting, or even experience front-end supply chain compromises. For instance, as documented in the 2023 Ledger Connect Kit exploit retrospective on Revoke.cash, a third-party JavaScript library vulnerability briefly affected dozens of Web3 front ends simultaneously. Knowing how to verify and revoke allowances at the command line or block explorer level ensures you are never dependent on a single website.
Method 1: Direct RPC Verification and Revocation via Foundry (cast)
If you want zero third-party front-end risk, you can query the token contract and submit a zero-value approval directly to an RPC node using Foundry’s cast command-line tool.
First, check the exact allowance a spender currently holds over your wallet by calling the read-only allowance(address,address) function (replace the placeholder addresses with the token contract, your wallet address, and the spender contract):
cast call 0xA0b86991c6218b36c1d19D4a2e9Eb0cE3606eB48 \
  "allowance(address,address)(uint256)" \
  0xYourWalletAddressHere \
  0xSpenderContractAddressHere \
  --rpc-url https://eth.llamarpc.com
If that command returns anything other than 0 (such as 115792089237316195423570985008687907853269984665640564039457584007913129639935), the spender has an active allowance. To revoke it directly from the terminal using your encrypted Foundry keystore or hardware wallet (--ledger), broadcast an approve call with the amount set to 0:
cast send 0xA0b86991c6218b36c1d19D4a2e9Eb0cE3606eB48 \
  "approve(address,uint256)" \
  0xSpenderContractAddressHere \
  0 \
  --ledger \
  --rpc-url https://eth.llamarpc.com
To revoke an NFT collection-wide operator permission (setApprovalForAll), pass false as the boolean argument:
cast send 0xNftCollectionContractAddressHere \
  "setApprovalForAll(address,bool)" \
  0xMarketplaceOperatorAddressHere \
  false \
  --ledger \
  --rpc-url https://eth.llamarpc.com
Method 2: Block Explorer Checkers (Etherscan and Blockscout Revokescout)
If you prefer a visual interface backed directly by block explorer infrastructure, use the native tools built into Etherscan and Blockscout:
- For Ethereum Mainnet (and sister explorers like Arbiscan, Basescan, Optimistic Etherscan, Polygonscan, and BscScan), navigate directly to Etherscan’s Token Approval Checker. Paste your wallet address, toggle between the ERC-20, ERC-721, and ERC-1155 tabs, connect your wallet via Web3, and click Revoke next to any outdated spender.
- For open-source multichain exploration, use Blockscout’s integrated Revokescout dashboard. Select your active network, connect your wallet, review your total value at risk, and submit the zero-allowance transaction directly inside the explorer interface.
Method 3: Multi-Chain Dashboards and Native Wallet Managers
When you need to audit a wallet across 10 or 15 EVM networks in one sitting, checking single-chain block explorers one by one is tedious. That is where dedicated multi-chain aggregators shine:
- The Revoke.cash dashboard supports over 100 networks, lets you filter by unlimited allowances, sorts permissions from newest to oldest, allows inline editing of allowance caps via the pencil icon, and maintains Revoke.cash’s historical exploit tracker so you can check if your address interacted with known compromised contracts.
- Rabby Wallet’s built-in approval manager is my preferred day-to-day browser extension because it surfaces every active contract, token, and NFT permission natively inside the wallet UI and supports batch revocation queuing without visiting an external website.
- MetaMask’s smart contract allowance revocation guide walks through managing spending caps through MetaMask Portfolio, while De.Fi Shield’s contract scanner adds automated risk scoring for unfamiliar spender contracts.
Drawing on Bitbond’s deep dive into token approval checkers, here is how the leading permission management tools compare:
| Tool Name | Primary Interface | Supported Networks | Standout Security Capabilities |
|---|---|---|---|
| Revoke.cash | Web dashboard and browser extension | Ethereum, Arbitrum, Base, Polygon, BNB Chain, and 100+ EVM networks | Inline allowance editing, Permit2 expiration tracking, exploit checker, and real-time approval warning extension |
| Etherscan Token Approval Checker | Native block explorer utility | Ethereum Mainnet (plus BscScan, Polygonscan, Arbiscan, Basescan equivalents) | Direct explorer verification, ERC-20/721/1155 tab separation, at-risk balance calculation |
| Blockscout Revokescout | Built-in block explorer dapp | Ethereum, Optimism, Base, Gnosis, and Blockscout-supported rollups | Integrated directly into open-source block explorer interface with zero external site redirection |
| Rabby Wallet | Native desktop and browser wallet | All major EVM networks | Built-in approval dashboard sorted by contract risk, batch revoke queueing, pre-transaction simulation |
| MetaMask Portfolio | Web dashboard paired with wallet | Ethereum, Polygon, BNB Chain, Arbitrum, Optimism, Base | Custom spending cap input during approval signing and dashboard revocation |
| De.Fi Shield | Web security suite | EVM chains plus Solana | Automated smart contract risk scoring and high-risk vulnerability flagging |
My Six-Month Wallet Security Hygiene Routine
Treating your crypto wallet permissions like corporate bank signatories through a mandatory six-month audit cycle eliminates dormant smart contract risk before legacy protocols get compromised.
When I worked in institutional banking, our compliance division ran a mandatory semi-annual signatory audit every April and October. Every corporate account had a list of authorized signers and active vendor debit mandates. Twice a year, we pulled the master ledger, went line by line, and revoked the signing authority of every former employee and every vendor whose contract had concluded. We never waited for a dispute or a fraud alert to clean up the ledger.
I apply that exact same six-month routine to my crypto portfolio. You do not need to pay gas to revoke every single approval five minutes after making a trade on a blue-chip DEX that you use three times a week. However, leaving unlimited allowances open for months on end is an invitation to get drained. Here is the exact six-step hygiene protocol I follow every six months, synthesizing best practices from DeFi Intel’s 2026 token approval tutorial, Cwallet’s smart contract approval guide, and DEV Community’s breakdown of silent wallet drainers:
1. Audit Every Network Independently
Approvals are strictly scoped to a single blockchain network. Revoking a USDC approval on Ethereum Mainnet does nothing to an active USDC approval on Arbitrum, Base, Optimism, or BNB Chain, even though your wallet address is identical across all of them. During my six-month review, I switch networks systematically in Revoke.cash or Rabby and inspect every L1 and L2 chain I have touched during the prior two quarters. Because L2 gas fees typically cost less than USD 0.01 per transaction, there is zero financial excuse for leaving dormant approvals open on rollups. On Ethereum Mainnet, I execute my revocations on weekend mornings when base fees are lowest.
2. Purge All Unlimited Allowances on Idle Protocols
Look at every entry marked “Unlimited.” Ask yourself one question: “Will I use this exact smart contract again in the next 14 days?” If the answer is no (whether it is a seasonal airdrop claim contract, an NFT minting contract, a cross-chain bridge, or an older version of a DEX router like Uniswap V2 when you now use V3 or V4), click Revoke and set it to zero.
3. Right-Size Active Allowances at the Time of Signing
Prevention is cheaper than cleanup. Whenever a dapp prompts me to approve a token today, I never blindly accept the default uint256 max cap. Modern wallets like MetaMask, Rabby, and Zerion allow you to click “Edit” on the spending cap prompt and enter the exact numeric amount required for that single trade. If I am swapping 1,000 USDC, I set the custom spending cap to 1000. Once the swap executes, transferFrom consumes the full 1000 allowance, and my remaining on-chain exposure automatically drops to 0 without paying for a separate revocation transaction later.
4. Sweep NFT setApprovalForAll and Permit2 Permissions
Do not stop at the ERC-20 tab. Switch to your NFT approvals and revoke setApprovalForAll permissions for any marketplace where you do not currently have an active collection offer or listing. Then check your active Permit2 sub-allowances and revoke any expired or unfamiliar routers.
5. Segregate Your Wallet Architecture Into Three Tiers
Never mix long-term custody with experimental contract execution. I structure my self-custody the same way a bank separates its central reserve vault from its retail teller drawers:
- Tier 1 (Cold Vault Wallet): Hardware-backed address that holds long-term BTC, ETH, and stablecoin reserves. This address never connects to dapps, never signs
approveorpermitcalls, and only ever sends or receives simple native transfers to and from my Tier 2 wallet. - Tier 2 (Warm DeFi Execution Wallet): Hardware-backed address used exclusively for established, battle-tested protocols (Aave, Uniswap, Curve). This is the wallet that undergoes the strict six-month allowance audit.
- Tier 3 (Disposable Hot Wallet): Software or secondary hardware address funded only with the exact capital needed for a new mint, bridge, launchpad, or unfamiliar dapp. Even if a contract approved by Tier 3 turns out to be malicious, the blast radius is strictly capped to the small working balance inside that disposable address.
6. Bookmark Your Tools and Read Raw Transaction Simulations
Phishing groups actively buy sponsored search engine ads targeting keywords like “revoke crypto permissions” and “revoke cash” to lure panicked users onto lookalike drainer sites. Bookmark the authentic URLs for your block explorers and approval checkers now, before an emergency happens.
Finally, remember the golden rule of Web3 security: a legitimate revocation tool will only ever ask you to sign an on-chain approve(spender, 0) or setApprovalForAll(operator, false) transaction. It will never ask you to type your 12-word or 24-word seed phrase to “synchronize,” “validate,” or “unlock” your wallet, and a revoke transaction should never show an outgoing balance transfer in your wallet’s transaction simulation preview. Keep your keys offline, cap your allowances at the point of sale, and clean your on-chain ledger every six months.
Sponsored Partner: Volet.com
Looking for a simple, everyday way to buy, hold, and sell cryptocurrencies alongside your traditional currencies and payment cards?
- Read my full breakdown: Complete Volet Review on DoraMilen.com
- Get started right away: Open your free Volet account using my referral link